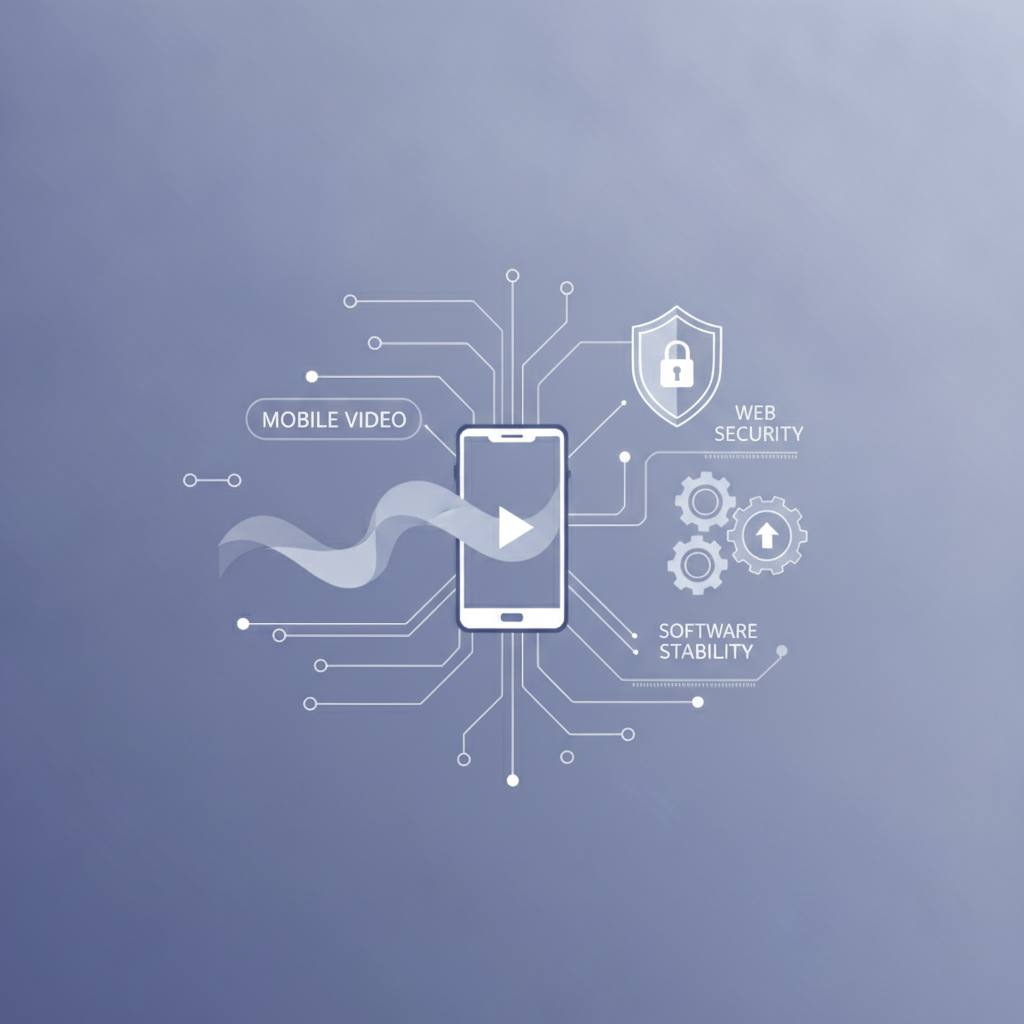
Mobile phones are rapidly becoming professional video tools, while web security challenges like XSS demand smarter defenses. Meanwhile, software development faces an ongoing battle with compatibility issues that will shape future coding practices.
The tech world continues its rapid evolution, and current trends show clear directions for the near future. On the hardware front, companies like vivo are pushing the boundaries of mobile photography and videography. The teased capabilities of the X500 Pro series, including 4K 240fps slow-motion, tell us that high-end smartphones are no longer just for communication and casual photos. They are becoming serious content creation tools, rivaling dedicated cameras. We expect this trend to accelerate. Future phones will likely feature even more advanced video processing, better low-light performance, and perhaps even integrated editing suites that leverage powerful mobile processors. The goal is to put professional-grade video production into the hands of everyday users, making high-quality content creation more accessible than ever.
However, as technology advances, so do its challenges. Web security remains a critical area. The persistent threat of Cross-Site Scripting (XSS), where malicious code can be injected via user input, highlights a foundational vulnerability. This problem is not going away; it will demand smarter, more integrated security solutions from developers and framework providers alike. We predict a future where web development frameworks offer more robust, default protections against such injection attacks. Expect more automated security checks during development and perhaps even AI-driven tools that identify potential XSS flaws before they reach deployment. The emphasis will shift towards building security in from the start, rather than patching it later.
Finally, the intricacies of software development itself continue to evolve. The compatibility issues seen with .NET 10's InlineArray explicit size reveal the ongoing struggle to balance innovation with stability in complex programming environments. As frameworks add new features and optimize performance, managing backward compatibility becomes crucial. We anticipate a greater focus on rigorous testing methodologies and improved version control that can seamlessly handle legacy code. Framework developers will likely invest more in tools that help identify and resolve these subtle compatibility issues earlier in the development cycle. The aim will be to create more resilient software ecosystems that can adapt to new technologies without breaking existing applications, ensuring smoother transitions for developers and users alike.